---
updatedAt: 2025-09-25T02:01:11.000Z
agentTools:
projectIndex: https://gtidocs.readme.io/llms.txt
---
# ASM Google SecOps SIEM Integration
> 🚧 Special privileges required
>
> This feature is only available to ASM administrators.
[Google Security Operations (SecOps) SIEM (Security Information and Event Management)](https://cloud.google.com/security-information-event-management) provides threat detection and investigation with integrated threat intelligence. This integration allows Google SecOps to ingest data from Attack Surface Management (ASM). Specifically:
* [Entities](https://gtidocs.readme.io/docs/entities-guide) discovered by ASM are ingested as entity objects.
* [Issues](https://gtidocs.readme.io/docs/issues-guide) detected by ASM are ingested as events.
An ASM Issue represents a detected vulnerability or potential cyber security weakness in a customer’s infrastructure. Surfacing this information in Google SecOps SIEM provides greater visibility and awareness to the customer.
## Configure the Google SecOps SIEM integration
> ℹ️
>
> This integration only runs when a Collection Scan finishes. For example, if this integration is added on Monday, but the next applicable Collection Scan is scheduled for Tuesday, the integration runs on Tuesday when the Scan finishes.
1. From the **Projects and Settings** menu in ASM, select the appropriate Project then click **Account Settings**.
> ℹ️
>
> This integration is applied to the selected Project and all Collections that Project contains.
2. Click the **Integrations** tab.
3. Go to **Outbound Integrations** and click **Add New** next to **Google SecOps SIEM**.
4. In the **Google SecOps Credentials** section:
1. Update your **Ingestion API Endpoint**, if necessary. This defaults to `malachiteingestion-pa.googleapis.com`.
2. Enter your **Google SecOps Customer ID**.
3. **Upload** **Service Account Key**. This is a JSON file that has been provided to you by your Google SecOps representative.
4. > ℹ️
>
> Once the JSON file uploads successfully, you are notified.\
> 
5. Select an **Ingest Period** from the drop-down.
6. Select the minimum **Issue Severity** for issues to be ingested into Google SecOps.
> ℹ️
>
> * For example, if you select **Info**, all Issue Severities are selected meaning that issues of any severity are ingested.\* If no **Issue Severity** is selected, only Critical Issues are ingested as this is the default.
7. Click **Add Integration** to create the integration.
> ℹ️
>
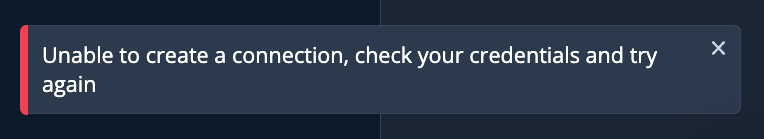
> When the wrong credentials are entered, the integration fails to connect.\
> 
## Find ASM Issues using UDM search
Once ASM Issues are ingested into Google SecOps, you can find them using the following UDM query in the Google SecOps UDM Search console: `metadata.product_name = "Mandiant Attack Surface Management"`